SMGSC Portal
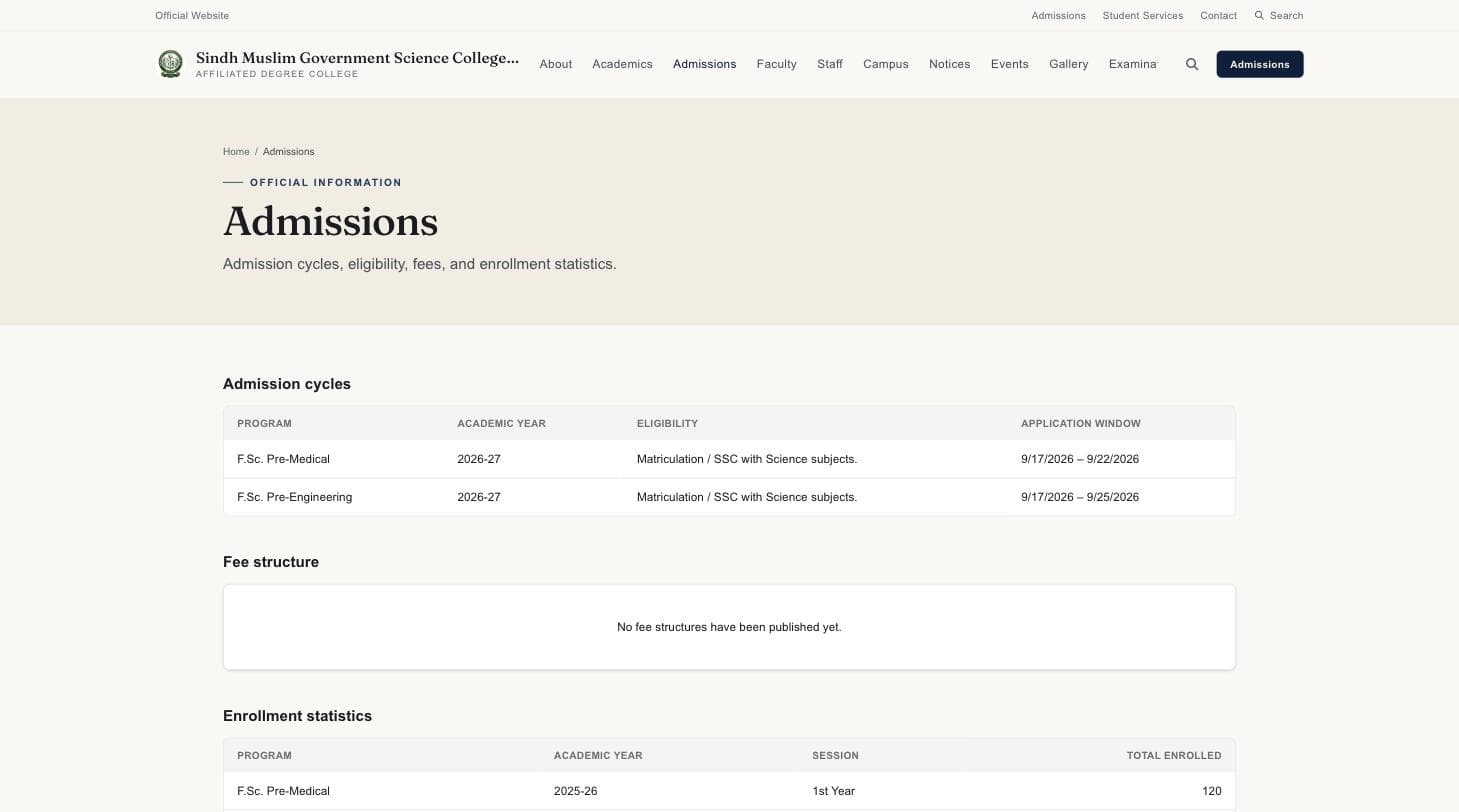
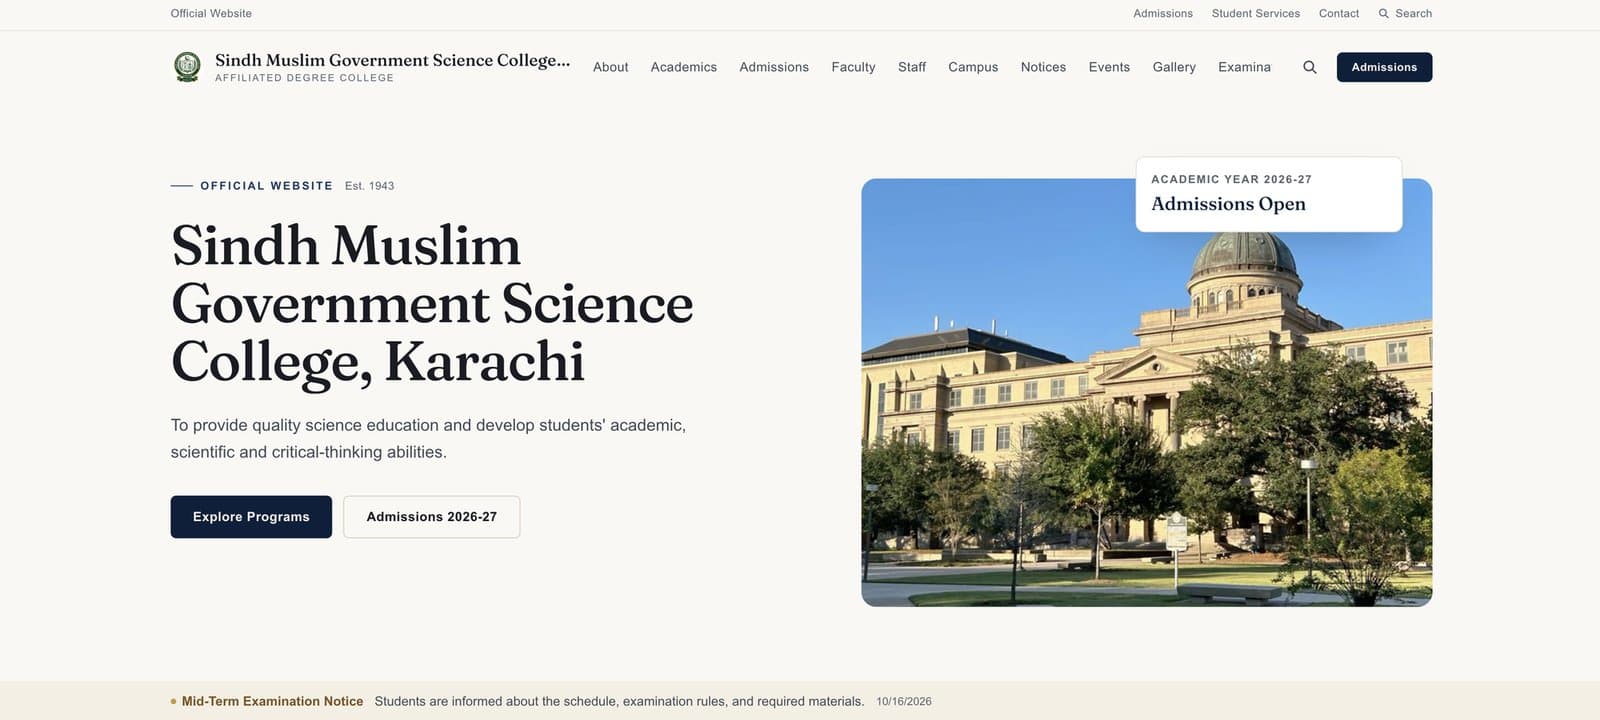
The official website and compliance back office for Sindh Muslim Government Science College, Karachi. Built to satisfy a real university circular where every published fact has to trace back to an approved, audited, human-verified source.
The Problem
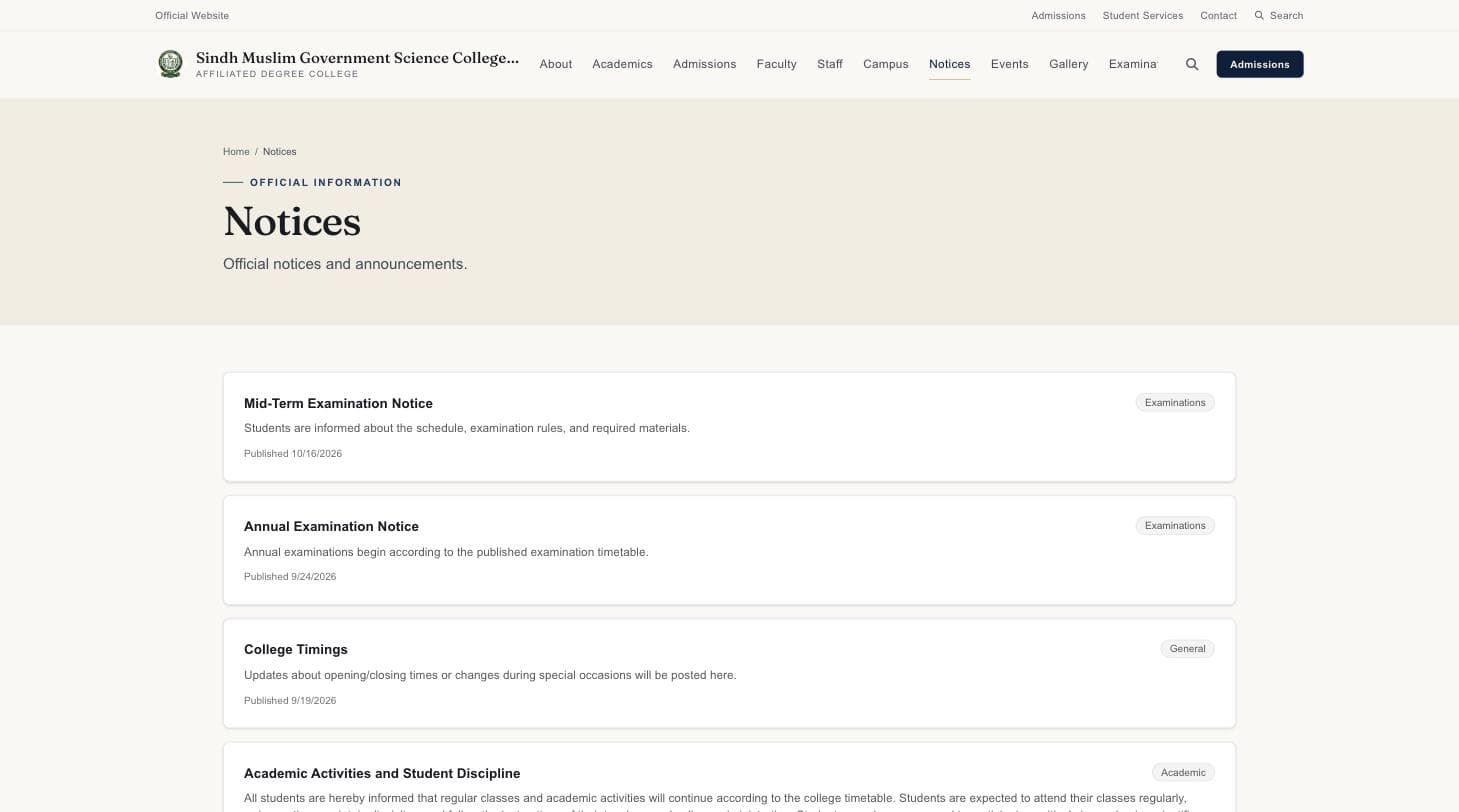
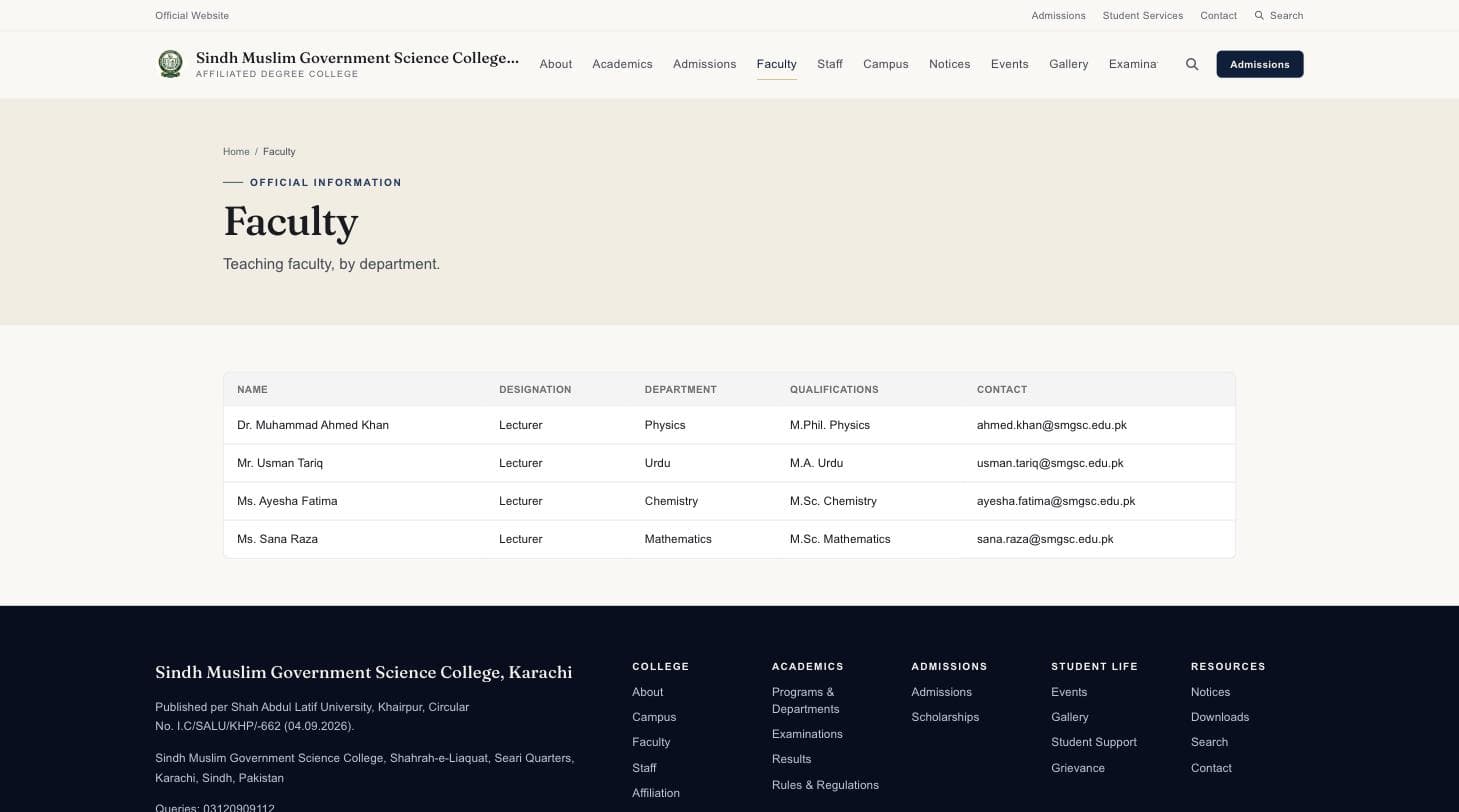
Shah Abdul Latif University's Office of the Inspector of Colleges issued Circular No. I.C/SALU/KHP/-662, requiring every affiliated college to publish an official website covering a fixed list of categories, including admissions, faculty, results, notices, and grievances, with accuracy held as the Principal's personal responsibility. That one clause rules out a static site someone edits by hand. It demands a system where every fact on the public page traces to a person authorized to publish it, and nothing goes live without a second person checking it first.
The Starting Point
A government circular, built from scratch, with no existing site or system to build on.
The Solution
A five-state content lifecycle (Draft → Submitted → Under Review → Approved → Published, with a reject-with-reason path back to Submitted) applies uniformly across every content domain, including notices, results, fee schedules, and faculty listings, instead of one-off logic per content type. The permission that lets someone author content (content:manage) is never granted to the same role as the permission that lets them publish it (content:publish), with exactly one break-glass exception (SUPER_ADMIN). Self-approval is structurally impossible, not just a review-checklist rule.
Architecture
Engineering Work
A database trigger makes every AuditLog row physically un-updatable and un-deletable, so immutability is enforced at the database layer rather than by application convention. Every route re-checks permissions server-side against the database on each request, never trusting a session cookie's claims. Official facts live in Postgres, never hard-coded, with isPlaceholder flags marking anything not yet confirmed by the college itself. A confidential grievance system encrypts submitter PII with AES-256-GCM at rest, with no public read path for case data, on top of rate limiting and a honeypot against automated submissions. No status can reach "verified" without a logged human decision; the system cannot self-certify. Dedicated accessibility and security passes shipped concrete fixes rather than just findings: axe-core caught a site-wide contrast failure across roughly 90 files and missing landmarks, and the security pass added per-IP login rate limiting, magic-byte upload verification, and a full CSP/security-header set. Every push runs lint, typecheck, the full unit and e2e suite against a real Postgres container, and a build-without-secrets check before it can ship.
AI Contribution
No AI is used in this product. It's included in the portfolio for its production-engineering rigor, not for AI usage.
Results
672 unit tests (Vitest) and 250 end-to-end tests (Playwright), 8 distinct admin roles, and all 20 items from the university's circular tracked to completion, running on $0/month across 3 free-tier services (Vercel, Neon Postgres, Cloudflare R2).
Final Product